Nearshore Portugal

Nearshore Portugal: The Compliance Case

Choosing a nearshore Portugal partner used to be a conversation about rates, time zones and English proficiency. In 2026 a fifth criterion appears in RFPs from regulated sectors with growing regularity: whether the development partner operates under the same regulatory framework as the client.

EUDI Wallet relying party

EUDI Wallet Relying Party: Integration Guide

Becoming a EUDI Wallet relying party is the part of eIDAS 2.0 that lands on engineering teams, and it is the part that has had the least attention. By 24 December 2026, every member state must make a compliant European Digital Identity Wallet available to its citizens and residents.

EU AI Act August 2026: What Actually Changed

EU AI Act August 2026: What Actually Changed

The EU AI Act’s enforcement date was August 2, 2026. Most of the coverage this week focused on what was delayed: the postponement of the high-risk obligations for employment decisions, credit scoring, and access to public services to December 2027.

CRA vulnerability reporting

CRA September 2026: 24-Hour Vulnerability Reporting

From 11 September 2026, every software manufacturer selling into the EU has to report an actively exploited vulnerability within 24 hours of becoming aware of it. Not 24 business hours. Twenty-four hours.

Claude Partner Network

Caixa Mágica Joins the Claude Partner Network

Caixa Mágica Software has joined the Claude Partner Network. This note explains what the partnership covers, how it fits our existing AI engineering work, and what it means for clients building on large language models under European regulatory constraints.

AI QA Testing for Regulated Industries: Qualigentic vs. Generic AI Tools

When a QA team at a bank evaluates AI testing tools, the conversation tends to start with the same set of questions that any engineering team would ask: how many test cases does it generate, how accurate is the generation, how well does it handle test maintenance, what frameworks does it support. These are legitimate questions. They’re also the wrong starting point, because they treat the problem of AI-assisted QA at a regulated financial institution as though it were the same problem as AI-assisted QA at a SaaS startup. It isn’t.

eIDAS 2.0 Implementation Guide: What Organizations Need to Do Before December 2026

Every EU member state must make a compliant European Digital Identity Wallet available by 24 December 2026, and regulated companies must accept it twelve months later. This guide covers what organisations have to decide, build and register before those dates, written from the perspective of a team that has maintained national eID middleware since 2011.

How Cabo Verde Built Digital Identity for an Archipelago

How Cabo Verde Built Digital Identity for an Archipelago

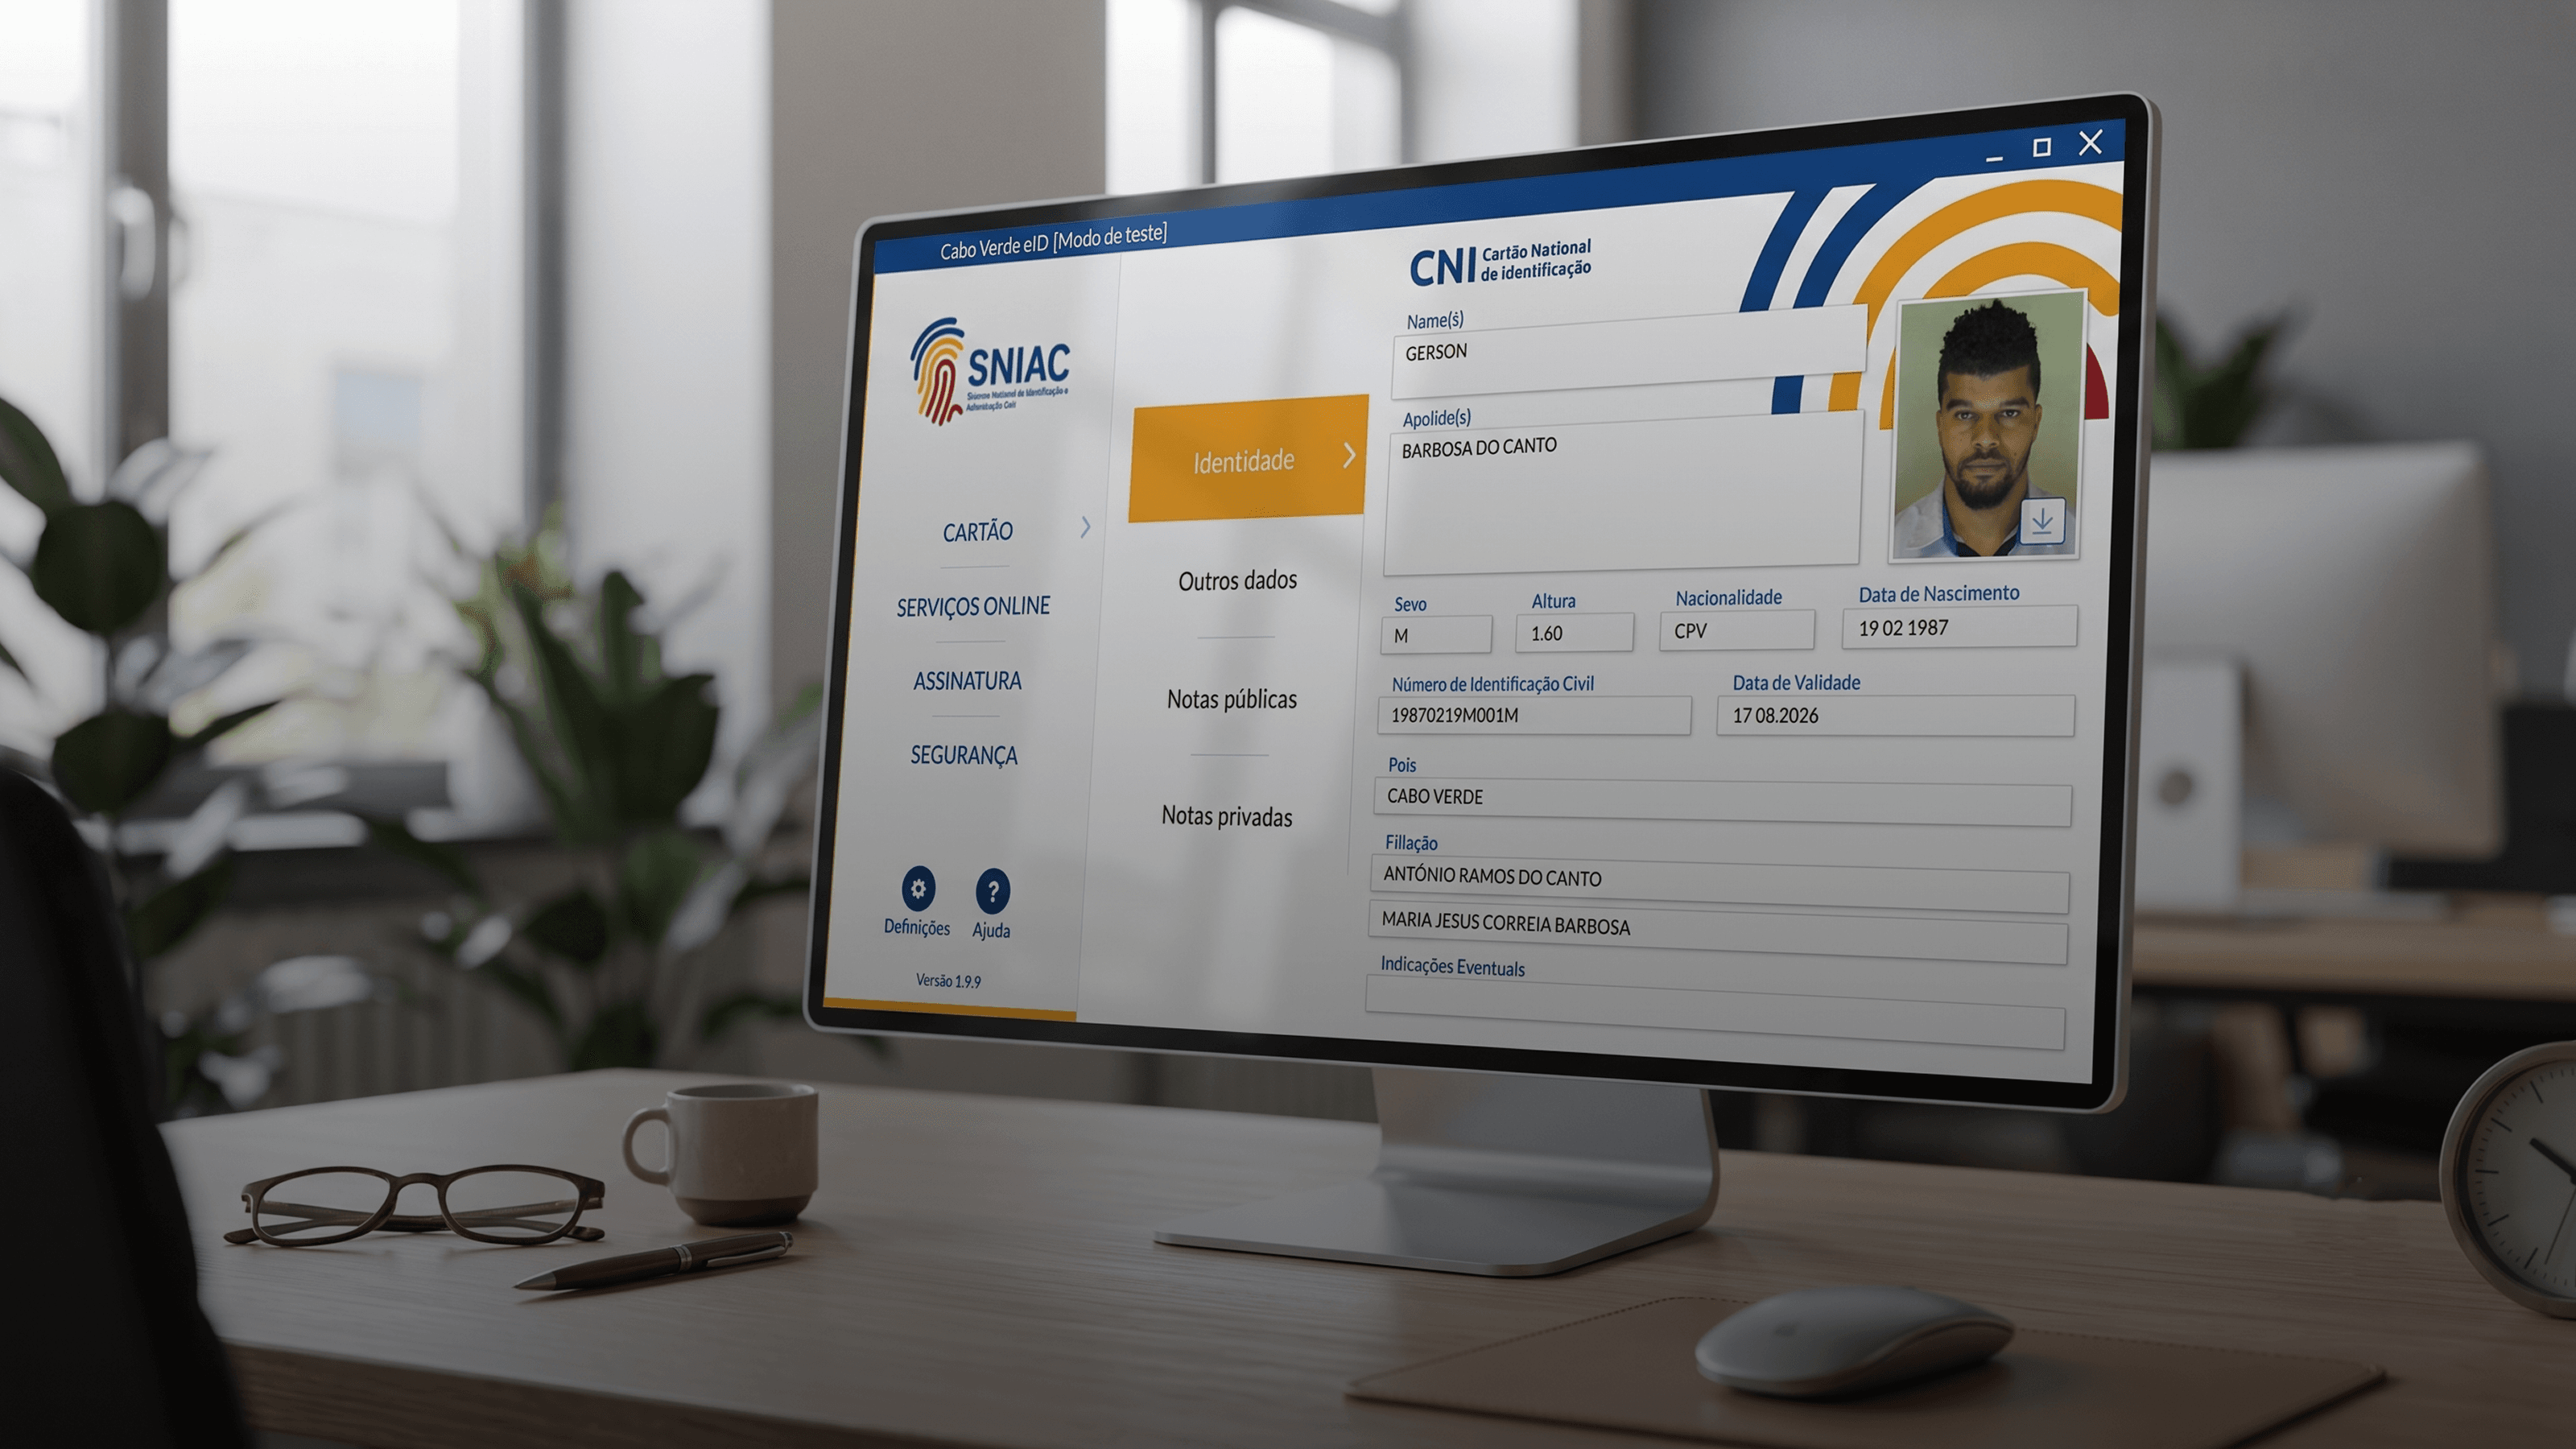
Most conversations about digital identity start from an assumption that’s rarely said out loud: that internet connectivity is stable, that service counters are close by, that population density turns infrastructure distribution into a problem solved by default. That’s a reasonable assumption in many European contexts. It simply doesn’t hold for a country like Cabo Verde — ten islands scattered across the Atlantic, where the distance between a citizen and the nearest public service can mean a boat trip, not a walk into town.